

 18 / 280

16
BLUE LABEL INTEGRATED ANNUAL REPORT 2014
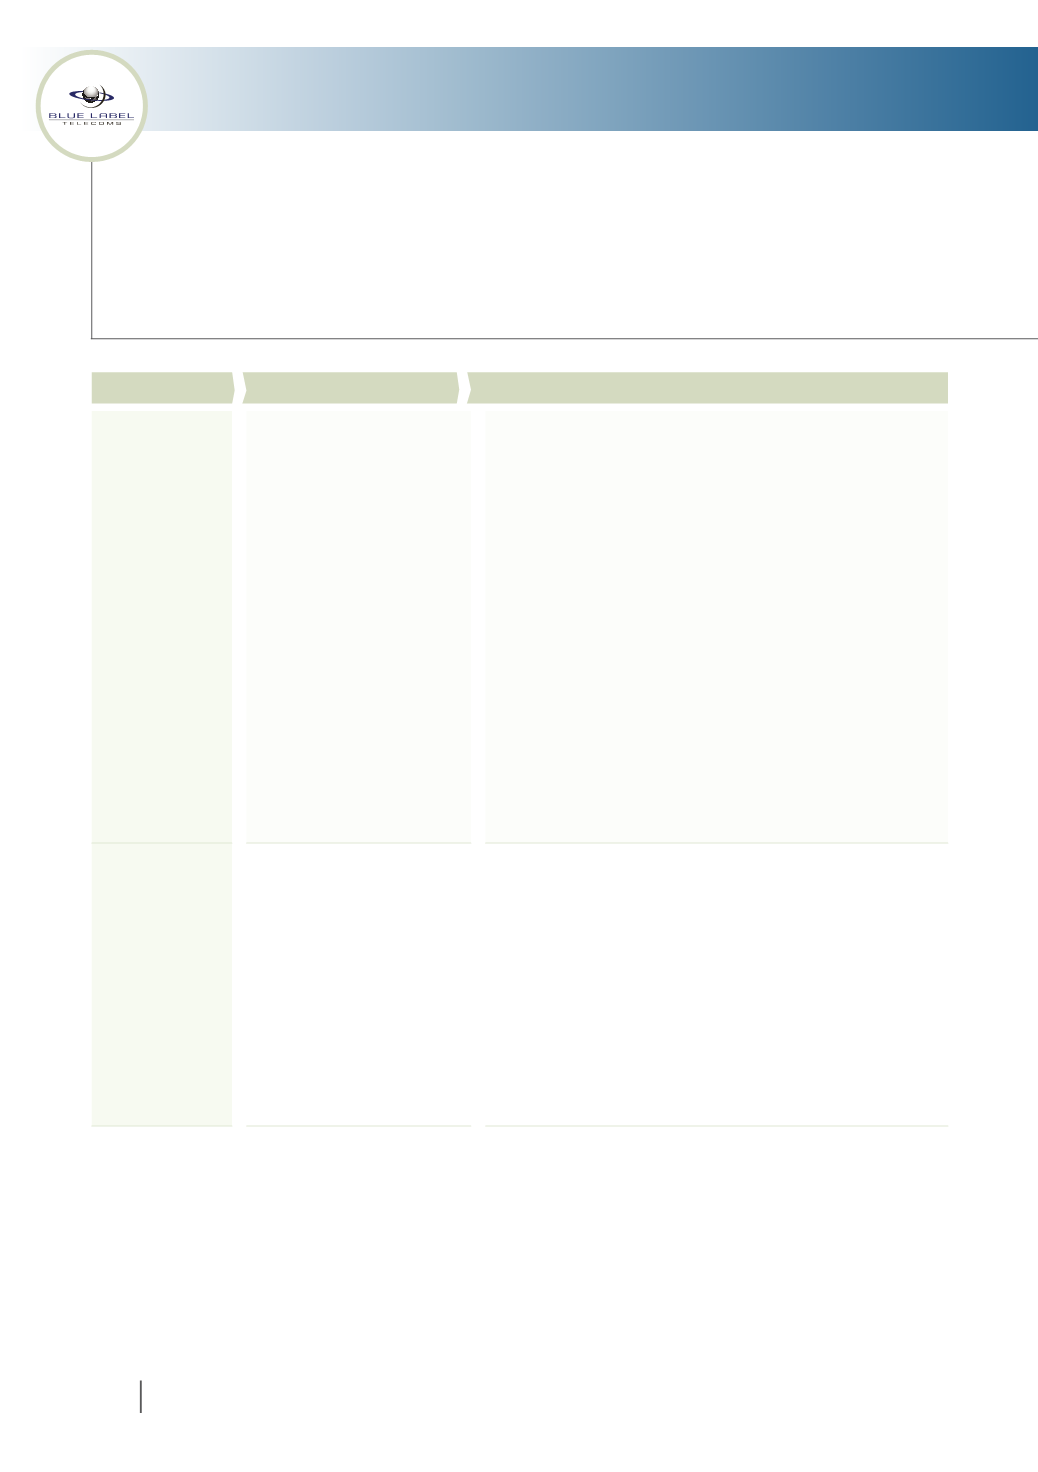
AIRTIME
MATERIAL IMPACTS
AND RISKS
CONTINUED
Risk
Context
Mitigating factors
Ability to
attract and
retain skilled
resources
The Group’s future
performance will depend
largely on the efforts and
abilities of its key
personnel and employees.
The existing executive
management at Blue
Label pioneered the mass
prepaid market and
established the Group’s
business model. Blue
Label’s future success will
depend, in part, upon its
ability to continue to
attract, retain, motivate
and reward personnel,
including executive
officers and certain other
key and specialised
employees.
The Joint Chief Executive Officers and co-founders are both
substantial shareholders and are passionate about and
dedicated to the sustainability and growth of the Group.
Key members of the management team are bound by service
and restraint agreements and in many instances are
shareholders of Blue Label. Executive management has
implemented talent management and succession planning in
key areas of the Group. Appropriate skills transfer activities are
ongoing through on the job and other training programmes.
The Remuneration and Nomination Committee has
approved remuneration policies which include long-term
retention benefits and short-term incentives. In addition,
key components of the Group’s Remuneration Policy have
been adjusted to focus on retention.
Increasing
exposure to
issues such as
data security,
breaches in
technology
security or
privacy
As the bulk of the Group’s
inventory is of a virtual
nature, defence against
cybercrime is a top priority
as susceptibility to hacking
and the penetration of
firewalls are always
matters of extreme
concern.
The Group is significantly dependent on the systems and
platforms that it utilises to deliver its products and services,
as well as to manage its merchant base. Over the past few
years, Group technology spend has been increasing in
recognition of this key imperative, in order to support not
only significant growth in the business (and the concomitant
rise in the number and type of transactions processed), but
also to improve system availability and robustness. This
invariably includes a major focus on the security of all
systems, both production and enterprise, in order to suitably
detect and manage security threats, as well as the ability to
recover from damage that may be caused as a result of
security-related incidents.